Shamem Ahmad
Cybersecurity Specialist & Security Engineer
Cybersecurity engineer with over a decade of technical experience in penetration testing, vulnerability assessment, and web application security. Focused on identifying architectural flaws, performing rigorous source code reviews, and building defensible system perimeters for growing and enterprise organizations.
HackerOne Platform Track Record
Verified responsible disclosure metrics, competitive bug bounty resolutions, and platform achievement badges earned as @blkryd.
Earned HackerOne Badges(7 total)
HackerOne VerifiedWaited more than six months for a report to get resolved.
Submitted valid reports 6 months in a row.
Was the first of multiple reporters to report a vulnerability.
Engineering Trust & Digital Sovereignty
Operating across penetration testing, static source code audits, threat detection, and continuous defensive hardening in alignment with European cybersecurity standards.
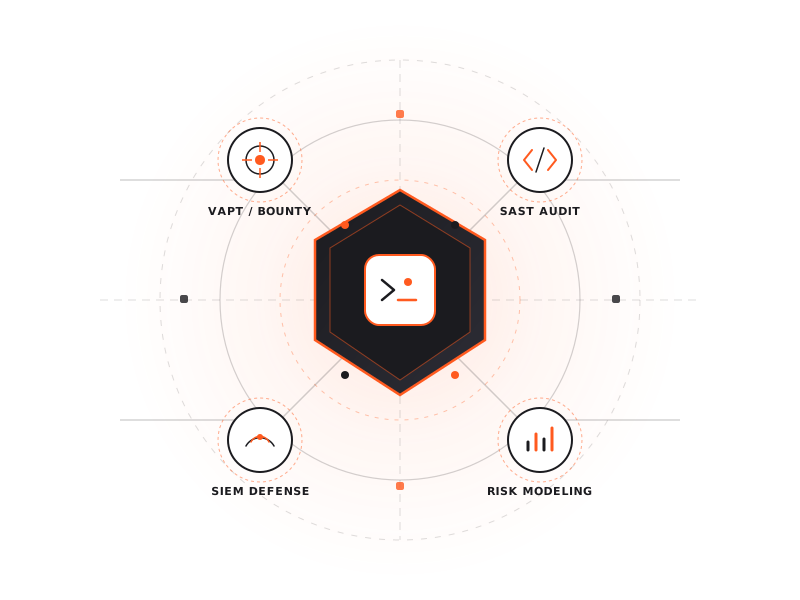
Offensive Assessment & Testing (VAPT)
Black-box, gray-box, and white-box penetration testing covering OWASP Top 10, logic bypasses, API endpoints, and privilege escalation vulnerabilities with standardized CVSS v3.1 reports.
Defensive Triage & Source Code Audits
Static source code review (SAST), real-time log forensics, SIEM telemetry correlation, and engineering-level remediation guidance that directly protects business operations.
Stationed in Ingolstadt, Germany. Strict compliance with GDPR, European NIS2 directives, and CEFR language standards.
Expertise & Arsenal
Standardized security methodologies, offensive evaluation toolsets, and enterprise defense frameworks.
Offensive Security & VAPT
Penetration testing & ethical exploitation
- ▸Vulnerability Assessment & Pen-Testing (VAPT)
- ▸Web Application Security (OWASP Top 10)
- ▸Network Penetration Testing & Reconnaissance
- ▸API Security & Authentication Auditing
- ▸Privilege Escalation & Exploit Verification
Code & Application Security
Static & dynamic security analysis
- ▸Source Code Review (SAST & DAST)
- ▸Vulnerability Triage & Remediation Guidance
- ▸CVSS v3.1 Impact & Exploitability Scoring
- ▸Secure Software Development Lifecycle (SSDLC)
- ▸Dependency & Supply Chain Risk Analysis
Defensive Operations & SIEM
Proactive threat detection & triage
- ▸Security Monitoring & SIEM Implementation
- ▸Threat Hunting & Indicator of Compromise (IOC) Analysis
- ▸Cybersecurity Incident Response & Containment
- ▸System, Kernel & Network Log Forensics
- ▸Endpoint Security & System Hardening
Cloud & Infrastructure Security
Perimeter defense & architecture
- ▸Cloud Security Posture & Architecture Review
- ▸Docker & Container Security Baseline
- ▸Identity & Access Management (IAM) Governance
- ▸Zero Trust Principles & Network Segmentation
- ▸Firewalls, Reverse Proxies & WAF Configuration
Security Automation & Tools
Scripting, tooling & Linux internals
- ▸Python for Security Tooling & Automation
- ▸Linux Server Administration & Hardening
- ▸Bash / Shell Scripting & Custom Exploits
- ▸Burp Suite Professional, Nmap, Wireshark
- ▸Git Workflow & CI/CD Security Gates
Risk Governance & Analytics
Data-driven risk reduction & metrics
- ▸Quantitative Cyber Risk Modeling
- ▸Operations Research & Optimization
- ▸Threat Modeling & Attack Surface Mapping
- ▸Compliance Alignment & Technical Reporting
- ▸Cross-Functional Engineering Collaboration
Career Record & Engineering Roles
Chronological audit of cybersecurity positions, hands-on penetration tests, and operational defensive triage.
Leading project-based Vulnerability Assessment and Penetration Testing (VAPT) and in-depth source code analysis for diverse client applications.
- ▸Execute comprehensive penetration tests covering authentication bypass, access control, and business logic flaws.
- ▸Conduct rigorous static code reviews to detect injection vulnerabilities and insecure logic before deployment.
- ▸Author standardized vulnerability advisories with CVSS v3.1 scores, reproduction steps, and remediation roadmaps.
- ▸Partner directly with software development teams to validate patches and re-test remediated endpoints.
Assistant Programmer
•TIHDTCBSpearheaded threat detection, live security monitoring, incident response, and log analysis to defend critical organizational networks.
- ▸Monitored live system telemetry and network traffic to detect suspicious lateral movements and anomalies.
- ▸Orchestrated incident response procedures, isolating affected services and mitigating active threats.
- ▸Implemented defensive measures, firewall rules, and host hardening across enterprise servers.
- ▸Authored custom Python automation to accelerate security log triage and incident reporting.
Conducted enterprise VAPT and source code analysis to harden high-traffic fintech and telecommunication applications.
- ▸Evaluated attack surfaces across distributed client-facing systems, identifying high-risk exposures.
- ▸Provided actionable engineering recommendations with CVSS risk ratings for prioritized patching.
- ▸Supported development squads in integrating secure coding practices into everyday workflows.
Security Projects & Case Studies
Automated source code scanning pipelines, offensive assessment frameworks, and quantitative risk modeling.
VAPT & Application Security Assessment Framework
Structured penetration testing framework covering authentication mechanisms, API security, input validation flaws, and privilege escalation vulnerabilities with standardized CVSS v3.1 reports.
Automated Source Code Review & SAST Pipeline
Methodology and scanning automation to detect hardcoded secrets, injection vectors, and dependency vulnerabilities directly within continuous integration workflows.
Threat Detection & Incident Response Triage Engine
Custom Python utilities to ingest server and firewall logs, correlate attack patterns, and highlight high-confidence indicators of compromise for rapid triage.
Quantitative Cyber Risk Analysis Model
Mathematical modeling framework applying operations research techniques to quantify vulnerability impact, prioritize patching schedules, and optimize defensive resource allocation.
Language Proficiency (CEFR Standard)
Certified communication competence aligned with the Common European Framework of Reference for Languages.
English
CEFR B2 CertifiedProfessional working proficiency across all technical and interpersonal communication domains.
Endorsements & Recommendations
Verifiable evaluations by senior engineering colleagues and cybersecurity leads.
He is hardworking, reliable, and responsible. I highly recommend him for this position.
Rajib Kanti Pal
Verified ColleagueSenior Software Engineer • Zalando SE
I have known him for several years and can confidently recommend him as a dedicated, reliable, and responsible person.
Partha Sarthi Bishwas
Verified ColleagueSenior Security Engineer • Brac IT
Initiate Direct Dialogue
Available for security engineering roles, penetration testing audits, and European data privacy consultations.
Ingolstadt, Germany
Eligible to work in Germany and the European Economic Area (EEA).